Control what
AI agents can do.
The authorization layer between your AI agents and your systems. Every sensitive action is checked against policy - before it executes.
- Model-agnostic
- Works across agent stacks
- Every decision audited
100%
Of sensitive actions checked before execution
<10ms
Decision overhead in the request path
0
Standing credentials left with agents
5min
Default lifetime of a scoped credential
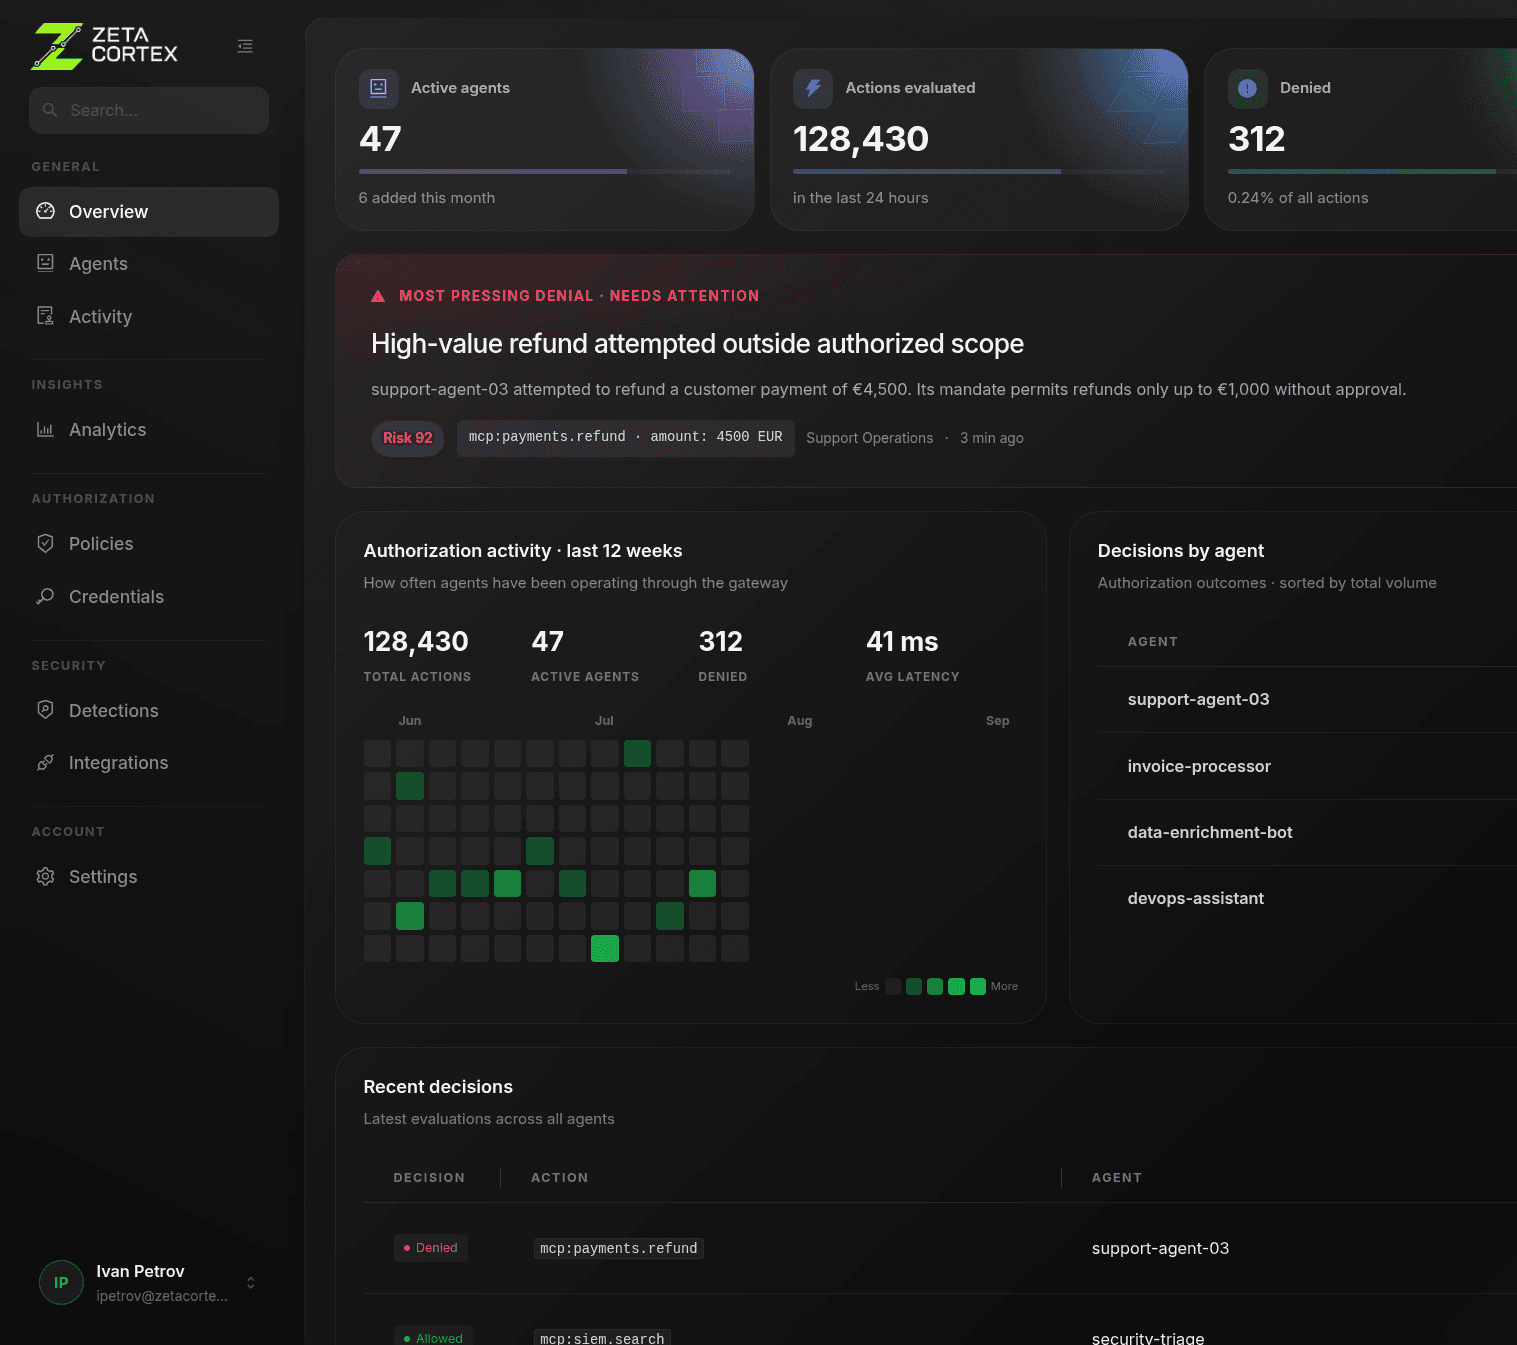
One console behind
every decision
Live authorization activity, per-agent outcomes, active credentials and the audit trail behind them - in one place.
- Every request, decision and execution in one timeline
- Per-agent breakdown of allowed, held and denied actions
- Active credentials visible and revocable in real time
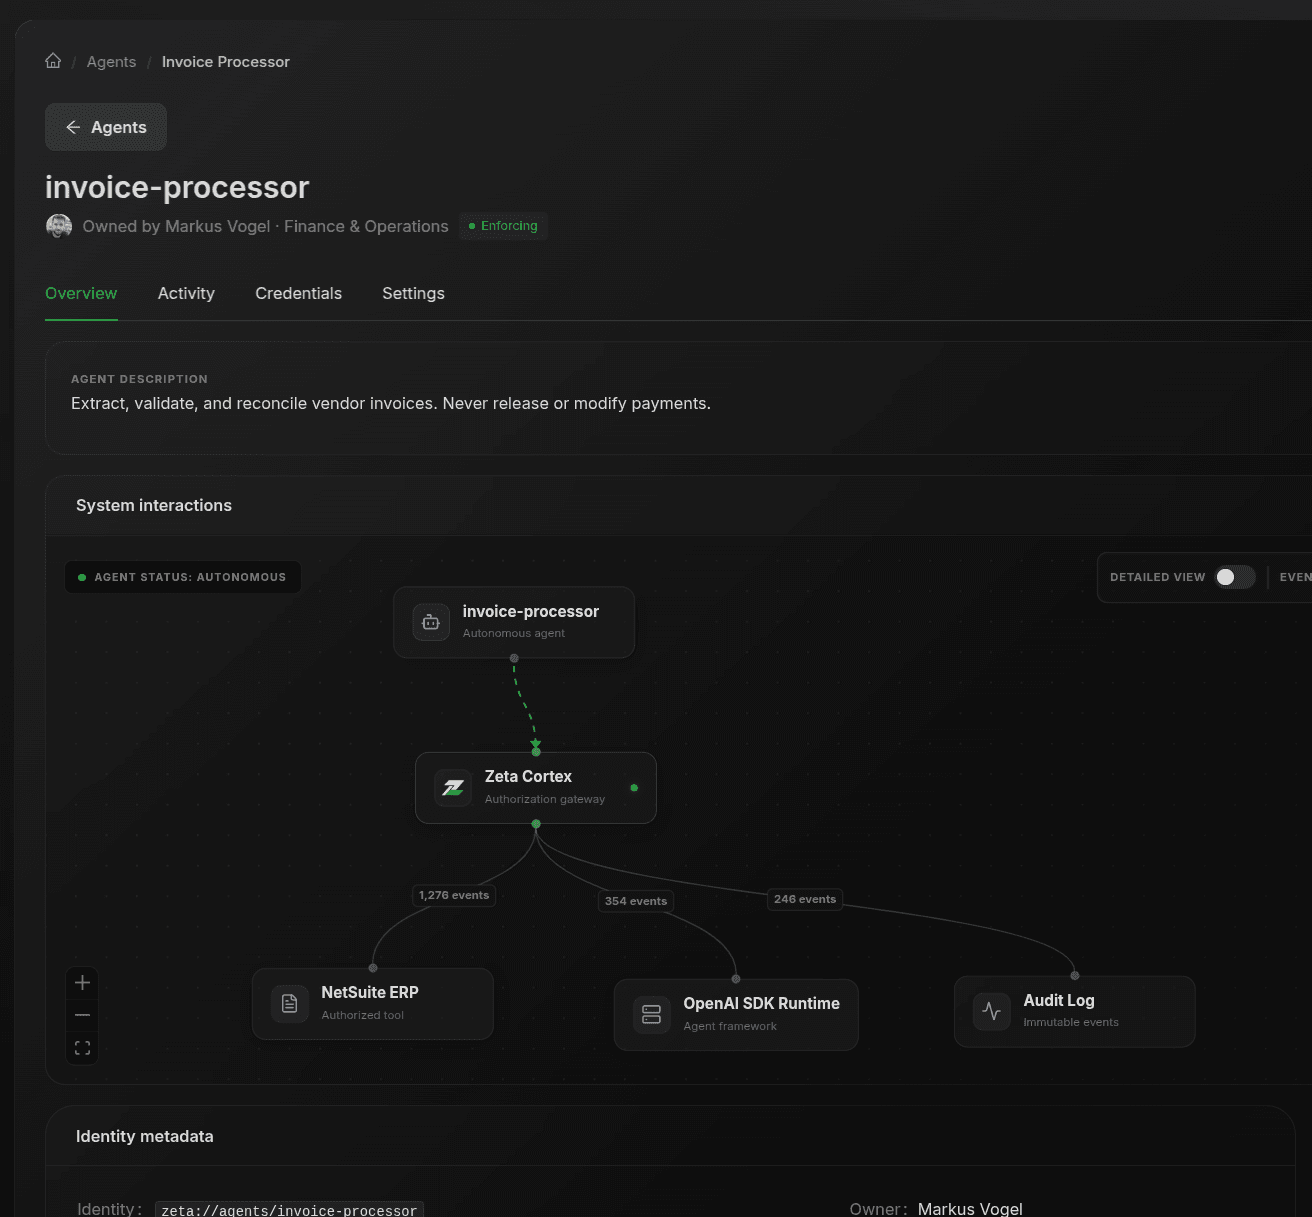
An identity for
every agent
Every non-human identity resolved to an owner, a purpose and the exact systems it's authorized to touch - with every interaction routed through Zeta Cortex and logged.
- Owner and purpose attached to every agent identity
- Authorized systems and tools scoped per agent
- Full interaction history for each non-human identity
Every action,
accountable.
Not a model transcript - an authorization history. What was requested, what was decided, who approved it and what actually ran.
Structured events for every decision, ready to route into the monitoring and compliance tooling your security team already runs.
- 12:07Executed
Deploy release v2.14 executed
12:07 · Deploy Agent → Production (EU) · approved by M. Okafor
- 12:04Approval required
Deploy held for approval
12:04 · Deploy Agent → Production (EU) · routed to platform on-call
- 11:58Allowed
Customer refund issued
11:58 · Support Agent → Billing · within the refund-limit policy
- 11:51Denied
Customer-data export blocked
11:51 · Data Agent → Warehouse · customer-data export policy
- 11:32Denied
Unidentified workload rejected
11:32 · Unknown workload → Payments API · no verified identity
Agents from anywhere. One authorization layer.
Zeta Cortex doesn't care where your agents were built - internal, framework-based, or vendor-shipped. They all pass through the same control before they touch anything real.

- Internal agents
- Agent frameworks
- MCP servers
- Enterprise copilots
- Browser agents
- Custom agents

- Cloud infrastructure
- SaaS applications
- Internal APIs
- Databases
- Business systems
Choose where it runs.
The control plane can live wherever your infrastructure does - hosted by us for the fastest path to production, or entirely inside your own cloud when agent traffic can't leave your boundary.
Hosted control plane
Fastest path to control. Policy, approvals and audit managed for you, with enforcement in the request path.
Hosted architectureYour cloud
Customer-controlled deployment for regulated environments - agent traffic and decisions stay inside your boundary.
Customer-cloud architectureAI agents are getting access.
Make every action accountable.
Zeta Cortex is in private development. Join the waitlist for early access and design-partner slots.