Platform
The control plane for agent authority
Five capabilities, one decision point. Zeta Cortex is not another agent builder - it's an independent security layer that protects agents wherever they were built.

Built to sit in the request path - and grow alongside your agents.
You keep the agent stack you have. Zeta Cortex adds the missing piece - an authoritative decision between your agents and everything they can touch.
1
decision point
every sensitive action passes through it
3
explicit outcomes
allow, hold or deny
0
standing credentials
access is scoped per authorized action
5
capabilities
one control plane, no per-agent guardrails
Agent Identity
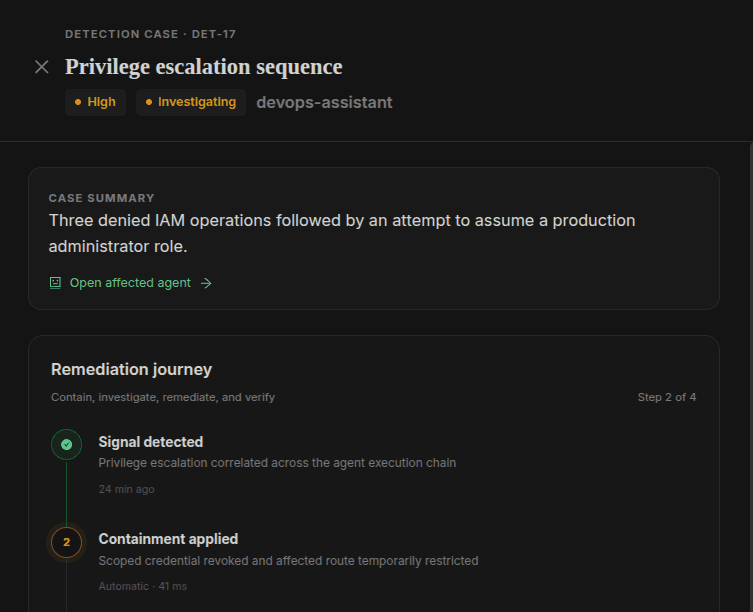
Before anything is decided, Zeta Cortex resolves who is acting: the agent, the workload it runs in and the person or team it acts for.
- No anonymous automation inside your environment
- Works the same for internal, framework and vendor agents
Policy Engine
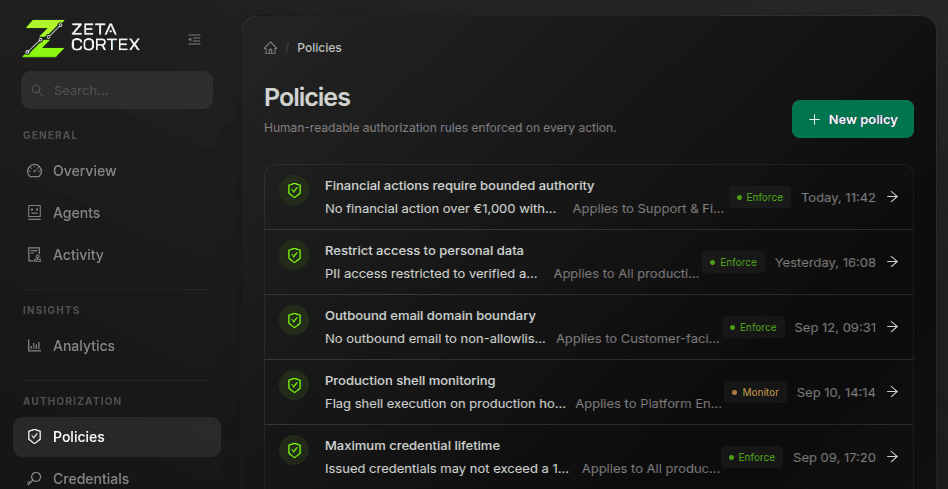
Your security team defines what each agent may do, against which systems, under which conditions. Policy decides what needs scrutiny - the agent doesn't get a vote.
- Rules by agent, action, target and context
- Owned by security, versioned and reviewable
Just-in-time Credentials
Agents shouldn't hold broad, permanent credentials. Zeta Cortex supports short-lived authorization scoped to the specific approved action.
- Credentials issued per authorized action
- Least privilege, enforced per request
Credential expires
Scoped to this deploy only. No standing keys.
Audit & Visibility
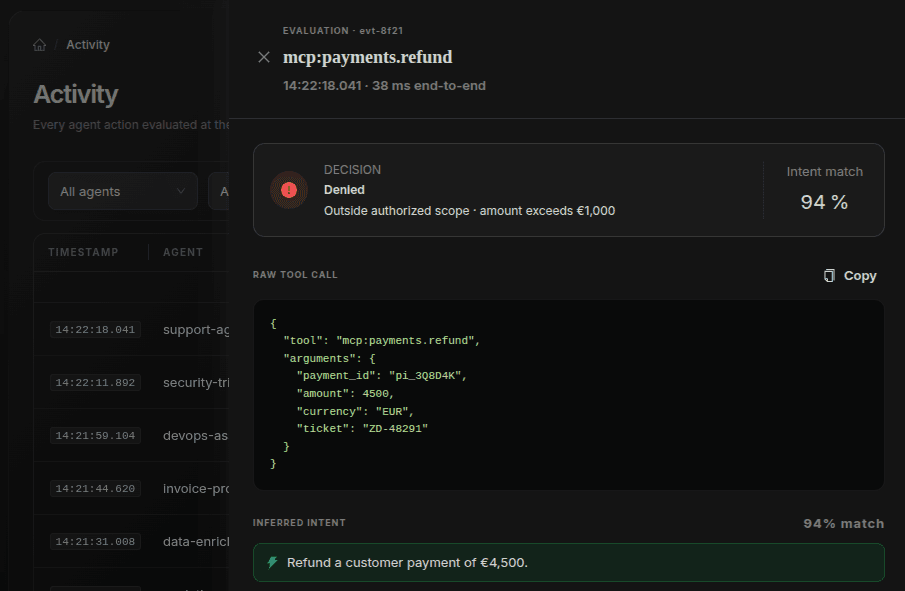
A complete authorization history: what was requested, what was decided, who approved it and what actually ran - so security teams can see what autonomous systems do.
- Requested, allowed, held, denied, executed - all recorded
- Structured events for the tooling you already run
Architecture
Built like security infrastructure
An enforcement point in the request path, a control plane that governs it and a deployment model that fits your boundary.
Step - 01
Sits in the request path
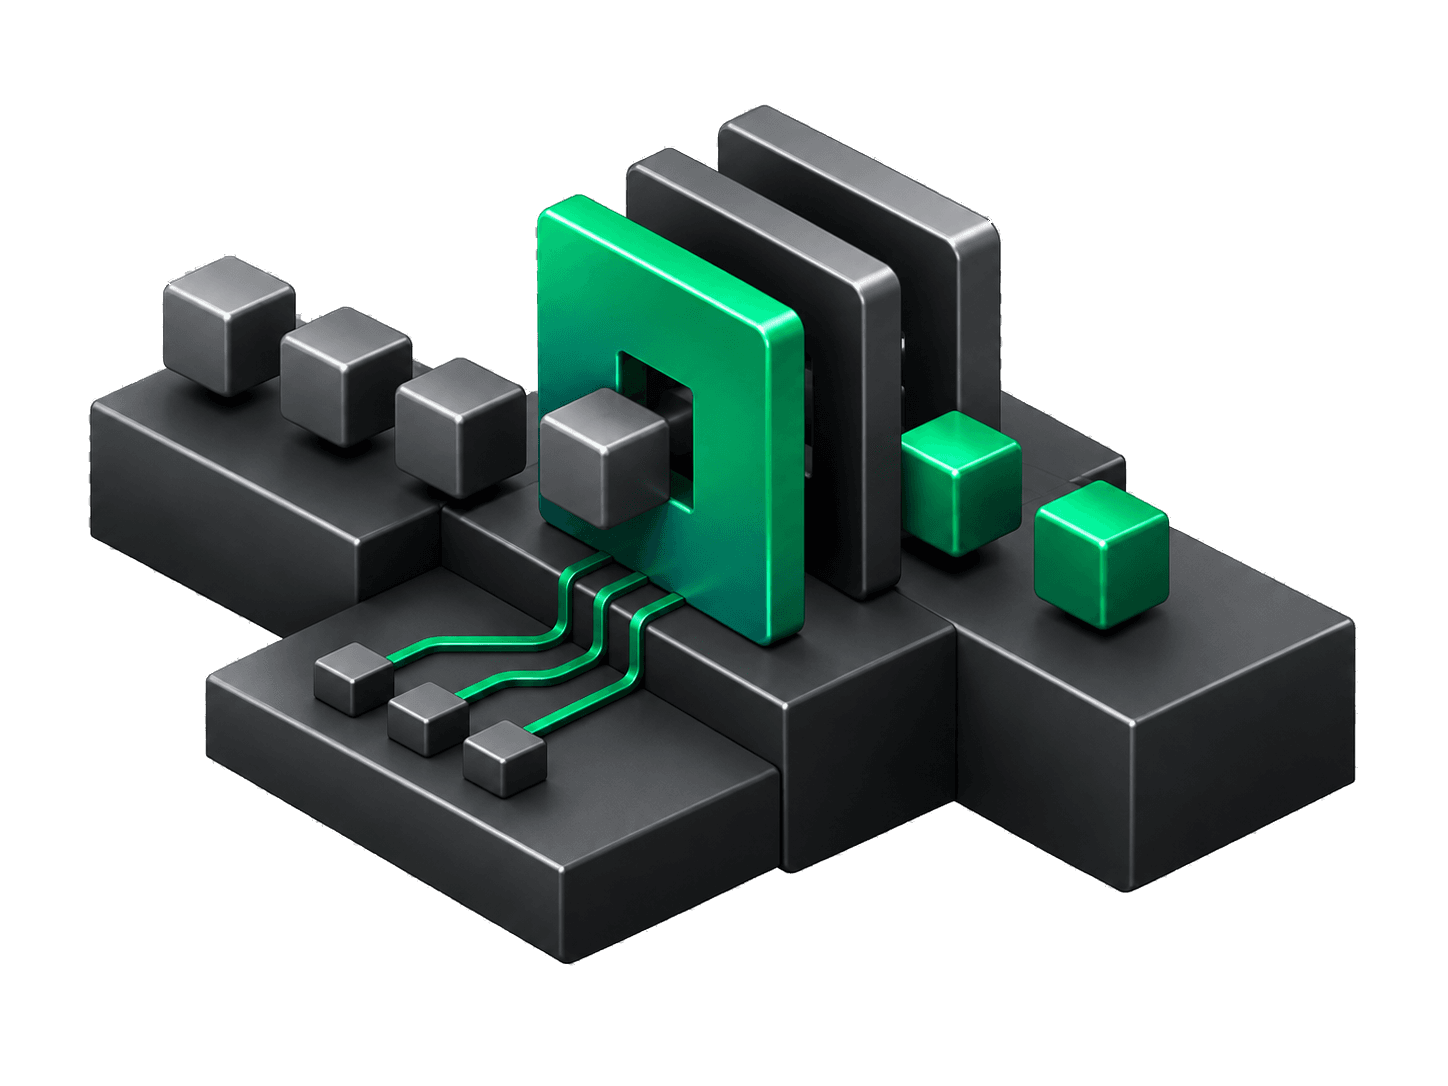
The enforcement point stands between your agents and the systems they call. Nothing reaches a target without a decision first - allow, hold or deny.
Step - 02
Decides locally, governed centrally
Policy and identity live in the control plane and sync down. Every decision is made next to your systems, so agent traffic never has to leave to be evaluated.
Step - 03
Hosted, or inside your cloud
Run the control plane hosted for the fastest path to production, or customer-controlled in your own VPC. Audit events flow to the tooling you already operate either way.
One boundary, your whole stack
Wherever an agent's next call is headed, it crosses the same decision point first.
Want early access?
Zeta Cortex is in private development. Waitlist members get access first, as capacity opens up.
Cloud & infrastructure
Deploys, configuration changes and provisioning actions on your cloud accounts.
SaaS & internal APIs
Billing, CRM, ticketing and the internal services your agents call.
Data & warehouses
Queries, exports and writes against the stores where customer data lives.
MCP servers & tools
Tool calls governed at the boundary, whatever server sits behind them.
Agent frameworks
Off-the-shelf frameworks and in-house orchestrators, treated exactly alike.
Vendor agents
Third-party agents get scoped authority too - not a copy of your admin token.